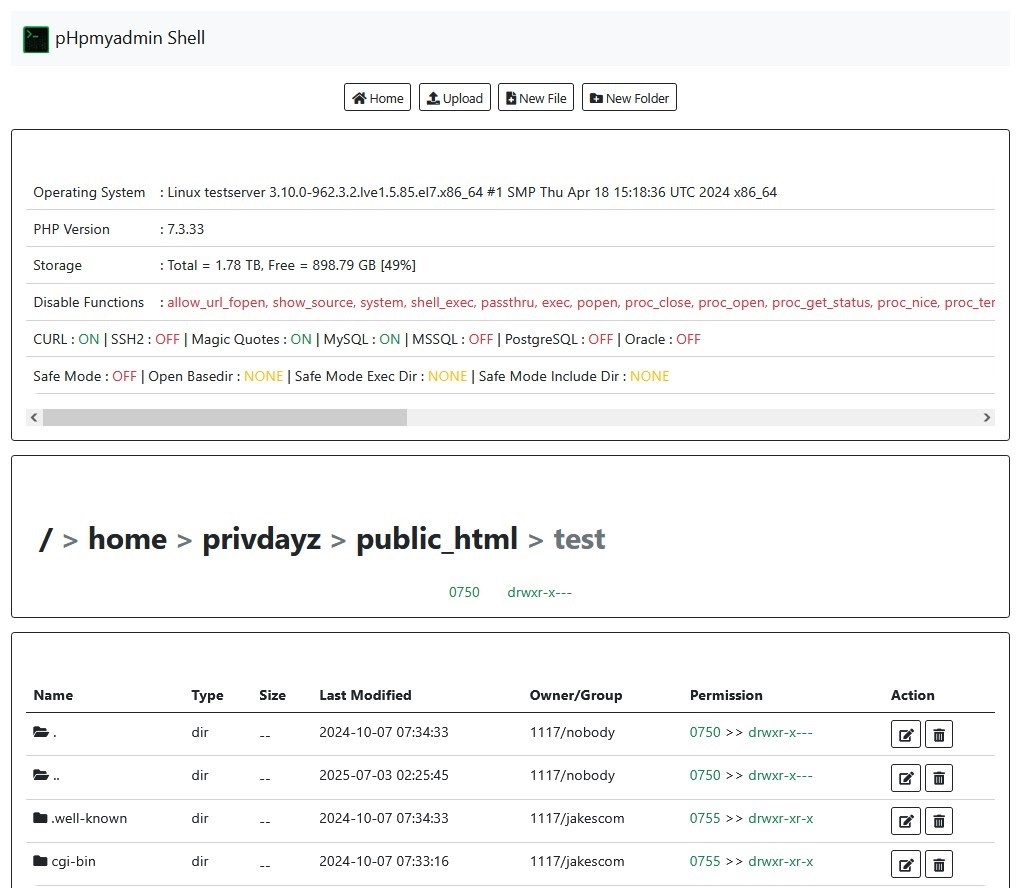
About this tool
Pure Bypass Engineering: Why This Shell?
Obfuscated Everything: Every critical function is hex-encoded, deeply randomized and reference-resolved at runtime. Static scanners? Dead on arrival. Cloud & Host Bypass: Built-in routines target Cloudflare, Imunify360, Wordfence, Litespeed, ModSecurity and more. Header overrides, request tricks, and anti-log tampering — on by default. File System Domination: Root-like file ops: recursive delete, hex rename, touch, chmod, recursive glob. Local disk info, auto-path normalization, hidden folder handling. Privilege Check & Root Escalation: posix functions and exploit checks for quick user/group recon, live suid/gid probing, and system pivoting. Zero Network Noise: No noisy callbacks, no forced external C2. You decide: fully local, or (if you want) drop your own connect-back in the editor. Live Command Execution: Multiple fallback chains: exec, system, passthru, shell_exec, popen, proc_open, COM (Windows). Nothing is blocked forever. Drag’n’Drop Upload, Modal File Edit: Ajaxless file drop, raw binary upload. Edit anything, anytime, in real-time. Filetype icons. Archive and database detection. Disk, User & Server Recon: Built-in disk free/usage stat, open_basedir, disable_functions, suid root binary scan, real user/group name resolution. Stealth First: 404 HTTP code on entry, robots noindex by default, all panel moves and ajax triggers obfuscated. File/folder names never in plain text. Shell-In-Shell: Upload your own PHP, Python, Bash payloads. Everything’s writable, everything’s hackable.
File & download
This tool must only be used on systems you own or have explicit written permission to test. Inspect the archive in an isolated virtual machine before running it.